Public repo
github.com
Christian-Katzmann
/dev-security
Local-first security observability for repositories that stay on your machine.
Remote
Christian-Katzmann/dev-securityDëvSec · v0.2.0 · Apache 2.0 · Open source
DëvSec runs practical security sweeps on your machine, keeps report history local, and turns scanner noise into a short list of next actions.
 github.com/Christian-Katzmann/dev-security
01 · Overview
DëvSec scanning itself. The 0.0 posture is real, and the top line is the one thing to fix first.
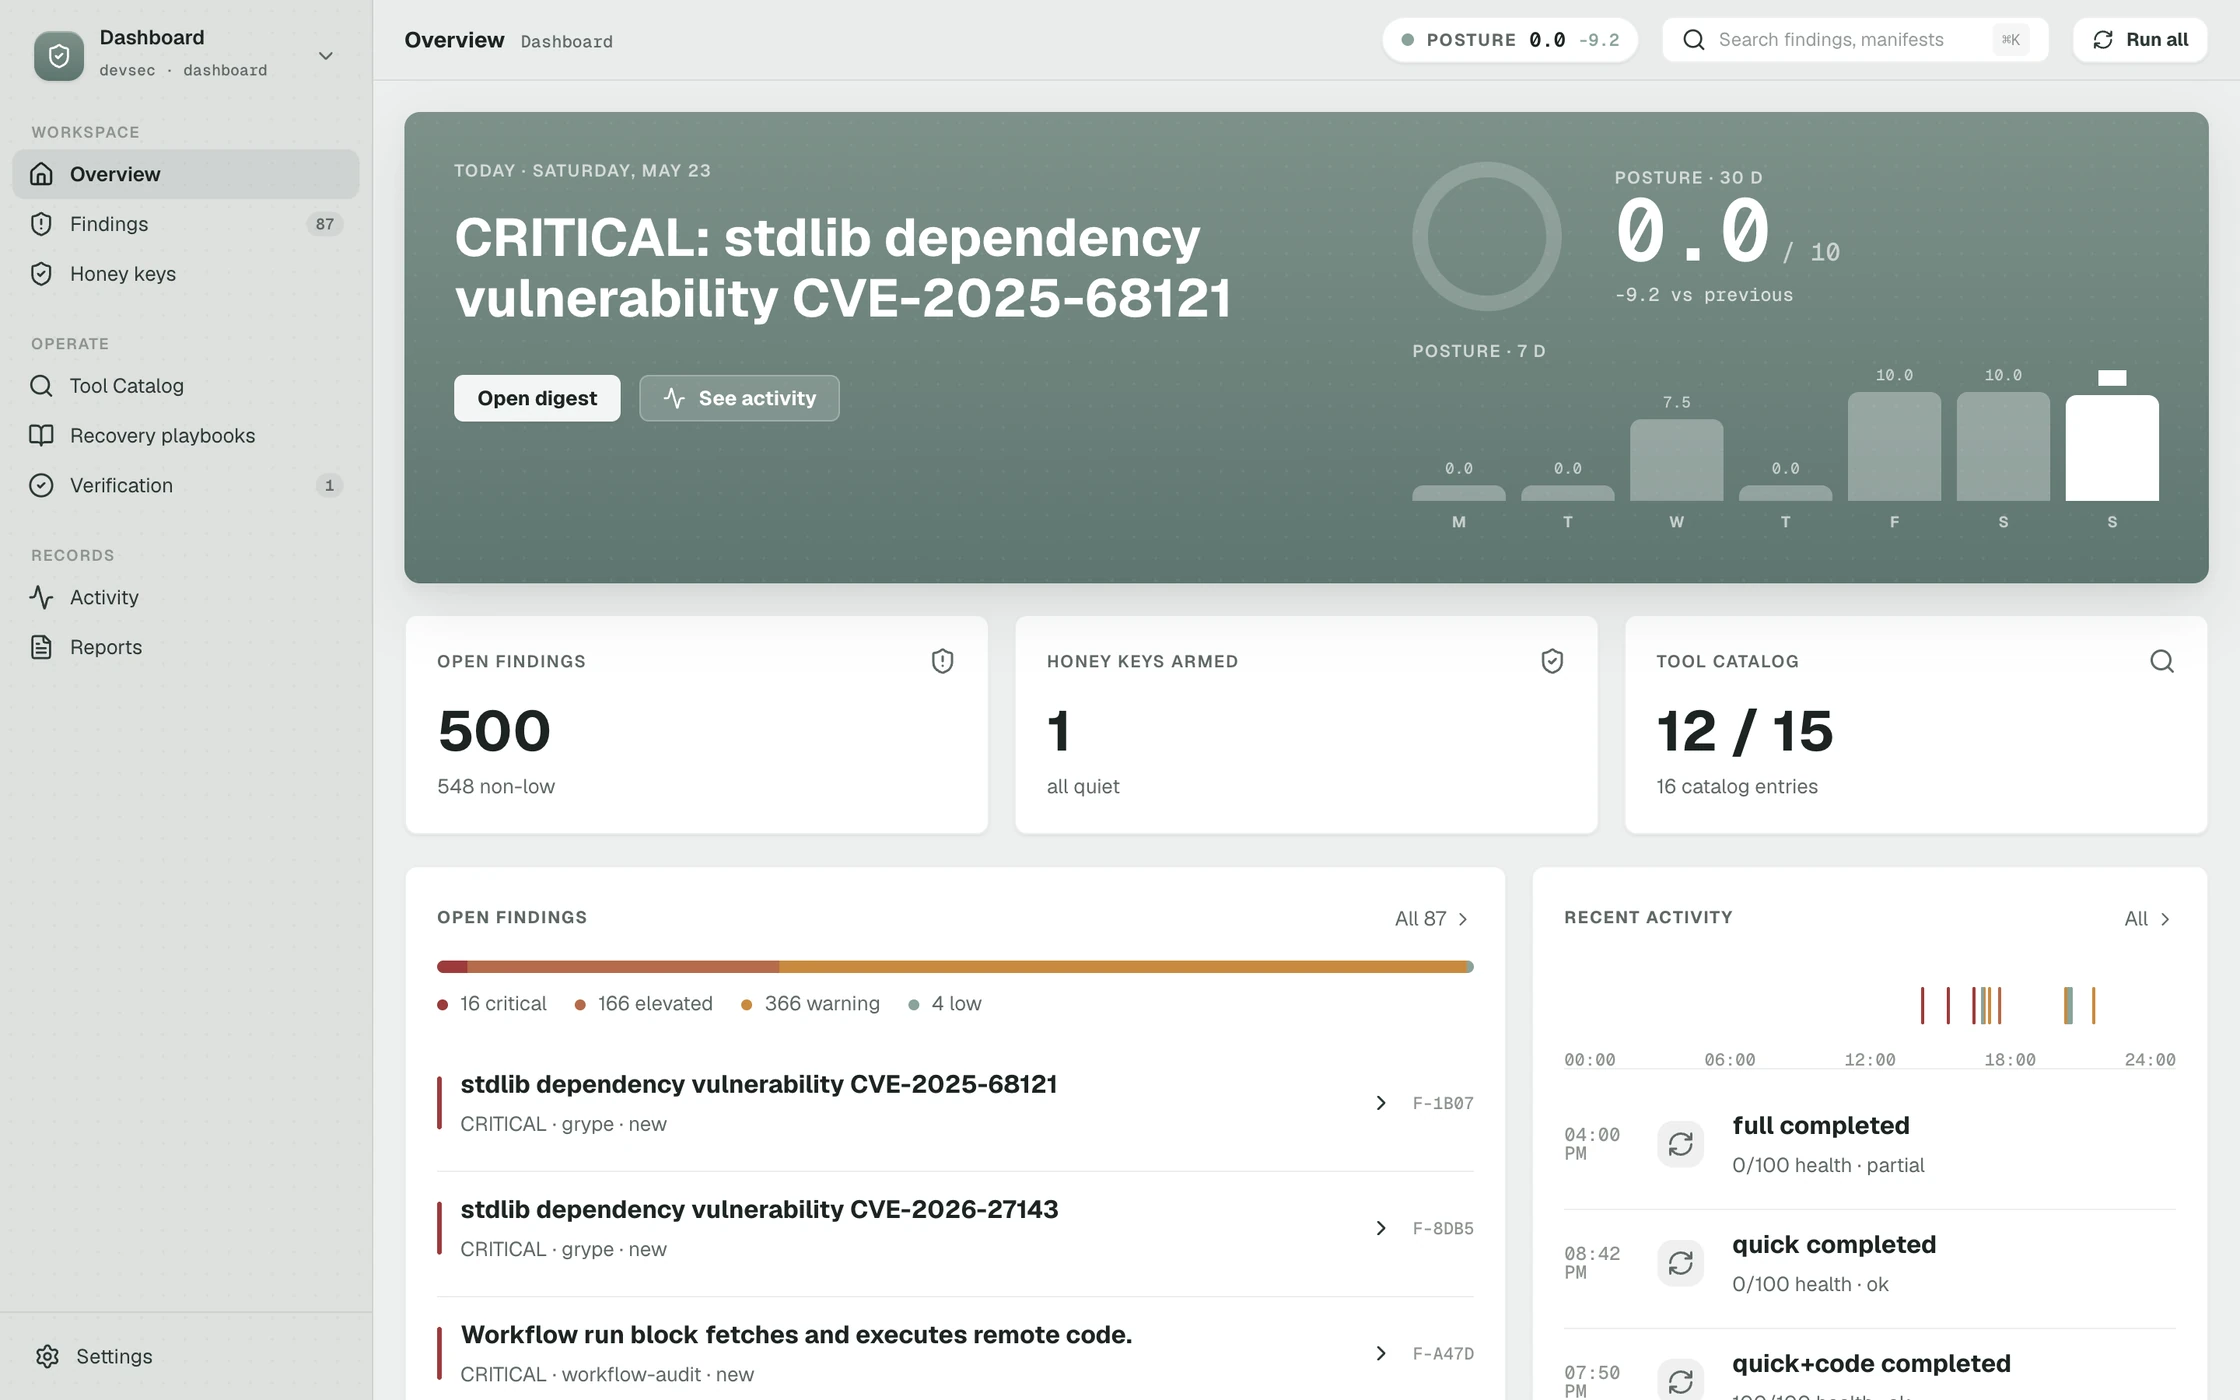
Overview · dev-security · 23 May 2026
Posture · 30 d
Posture · 7 d
Open findings
Activity · 24 h
Run established open-source scanners against repos on your machine. Source and reports stay under your control.
Scanner output is grouped into cases with severity, evidence, suggested fixes, and agent-ready handoff prompts.
Missing tools, partial scans, and evidence gaps are shown directly instead of being hidden behind a misleading score.
02 · 32 seconds
The trailer, without sound. Nothing in it is mocked.
03 · Cases
Scanners
run on the machine
Raw findings
deduplicated by fingerprint
Cases
risk, evidence, fix
Playbooks
steps and a time estimate
Next action
CRITICAL: stdlib CVE-2025-68121
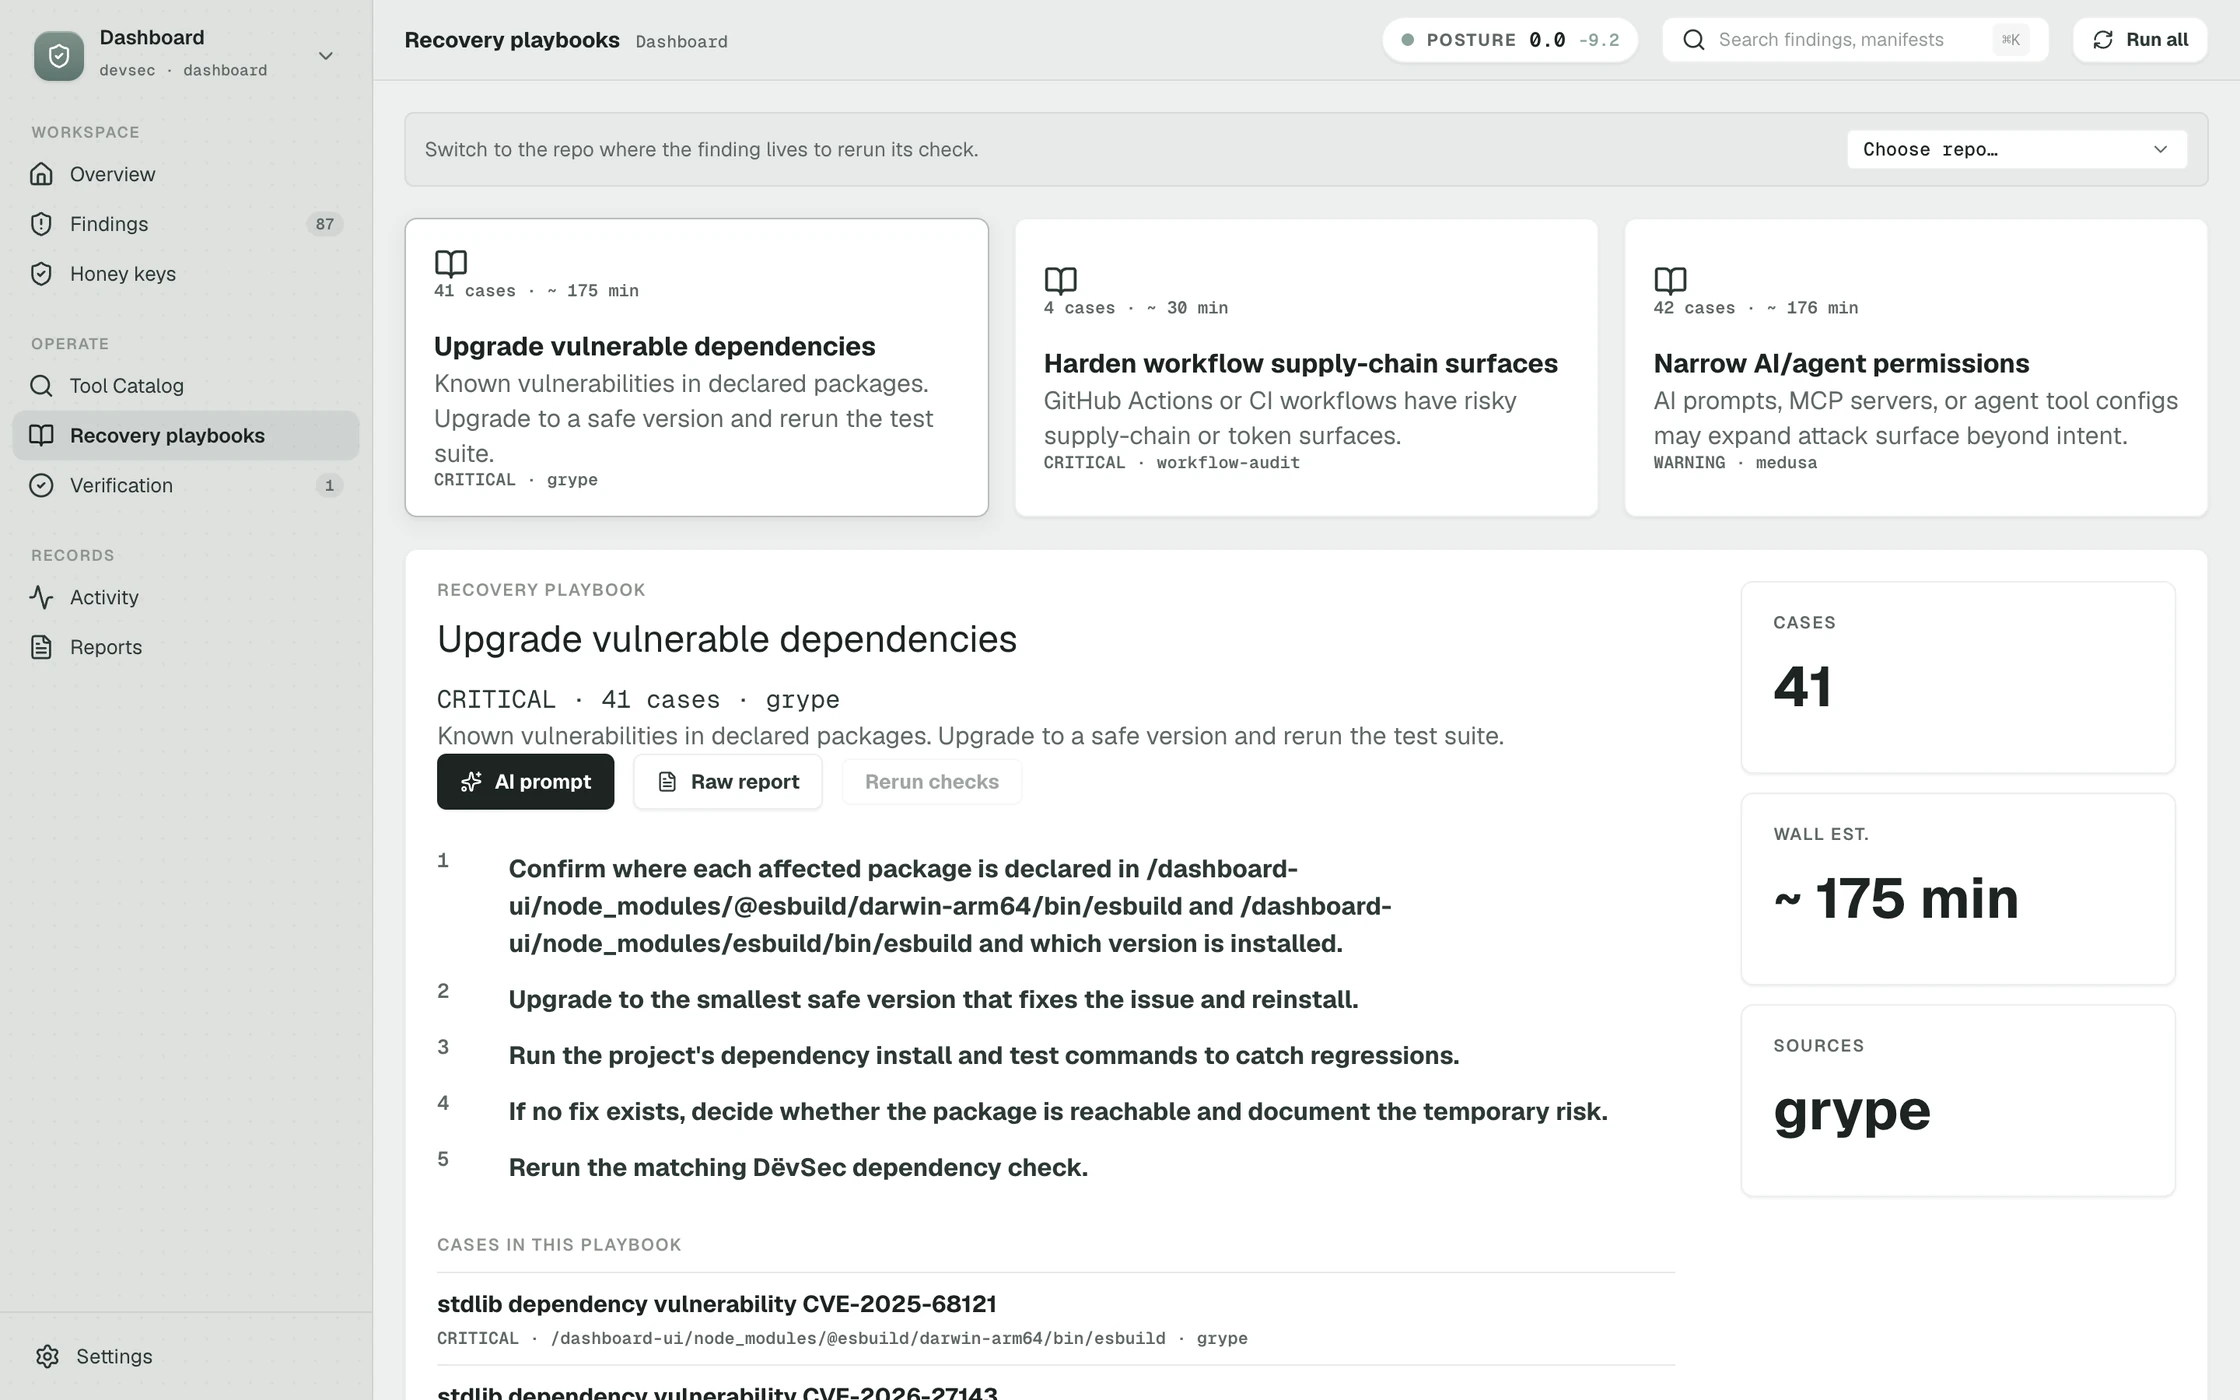
One job of about 175 minutes, with numbered steps. Not forty-one tickets.
A prompt for the agent you already trust, written on the machine. Verify first, then fix.
AI prompt · ready to copy
F-1B07
Case: stdlib dependency vulnerability CVE-2025-68121
Risk: A resumed TLS handshake can succeed where it should
      have failed.
Evidence:
- grype: CVE-2025-68121 in the Go stdlib inside
  dashboard-ui/node_modules/@esbuild/darwin-arm64/bin/esbuild
- Go advisory GO-2026-4337: crypto/tls, fixed in go1.24.13,
  go1.25.7 and go1.26.0-rc.3
Verification steps:
- Confirm the scanner result against that binary.
- Decide whether this is exploitable here, not just theoretically.
Fix steps:
- Rebuild on a Go release the advisory lists as fixed.
- Re-run the matching DëvSec dependency check.
04 · Install
The shortest path is still the most honest one: install locally, scan a repo, then open the dashboard on 127.0.0.1.
Read the docs[01]$git clone https://github.com/Christian-Katzmann/dev-security.git
→ Repository cloned · workspace prepared
[02]$cd dev-security
→ Entered isolated audit directory
[03]$./install-security-observatory.sh
→ Scanner toolchain ready · dependency cache warmed
[04]$security-scan .
→ SBOM generated · secrets checked · CVEs resolved
[05]$security-scan dashboard
→ Dashboard on http://127.0.0.1:8765 · nothing left the machine
Established open-source tools, each with a policy for network, credentials and file writes. A missing tool shows as missing.
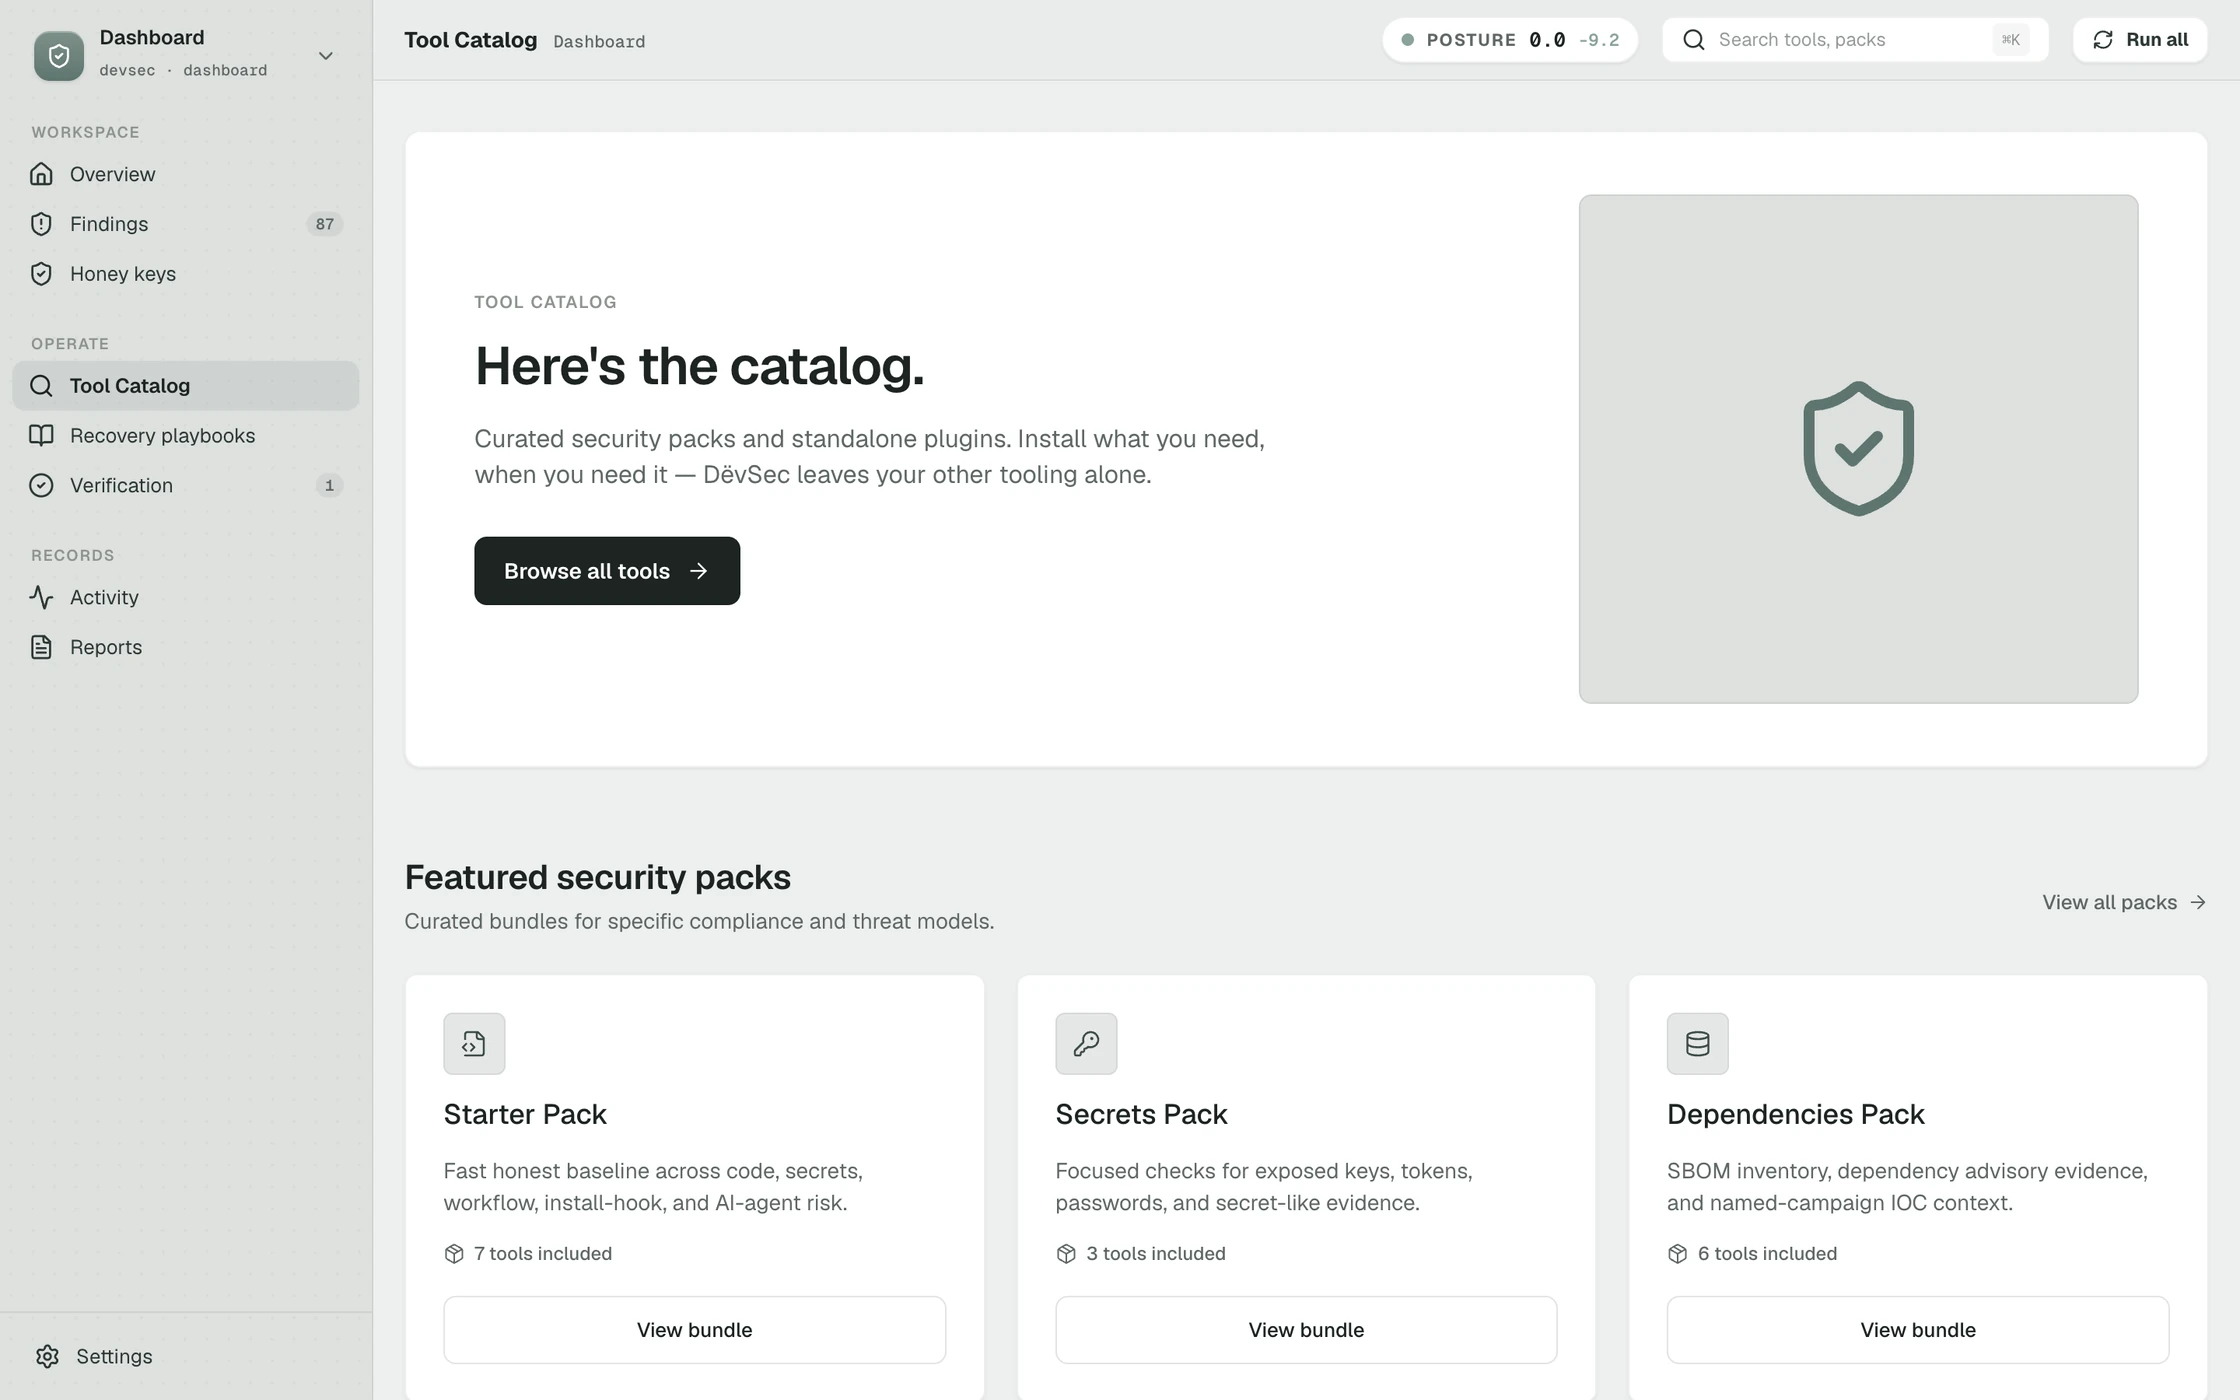
Tool Catalog · 12 of 15 tools ready
05 · Honey keys
A decoy key that authenticates to nothing. Use it, and the project turns critical.
Trace
What it refuses to do
06 · Trust boundary
Scanners, history and dashboard stay on the machine. Four network paths exist, all off by default.
Your machine
No upload, no telemetry, no licence server, no cloud model.
Opt-ins · off by default
07 · Repository
Public repo
github.com
Christian-Katzmann
Local-first security observability for repositories that stay on your machine.
Remote
Christian-Katzmann/dev-security