DëvSec · v0.2.0 · Apache 2.0 · Open source

Sëcure By Design™

DëvSec runs practical security sweeps on your machine, keeps report history local, and turns scanner noise into a short list of next actions.

github.com/Christian-Katzmann/dev-security

01 · Overview

The dashboard, scanning its own repository.

DëvSec scanning itself. The 0.0 posture is real, and the top line is the one thing to fix first.
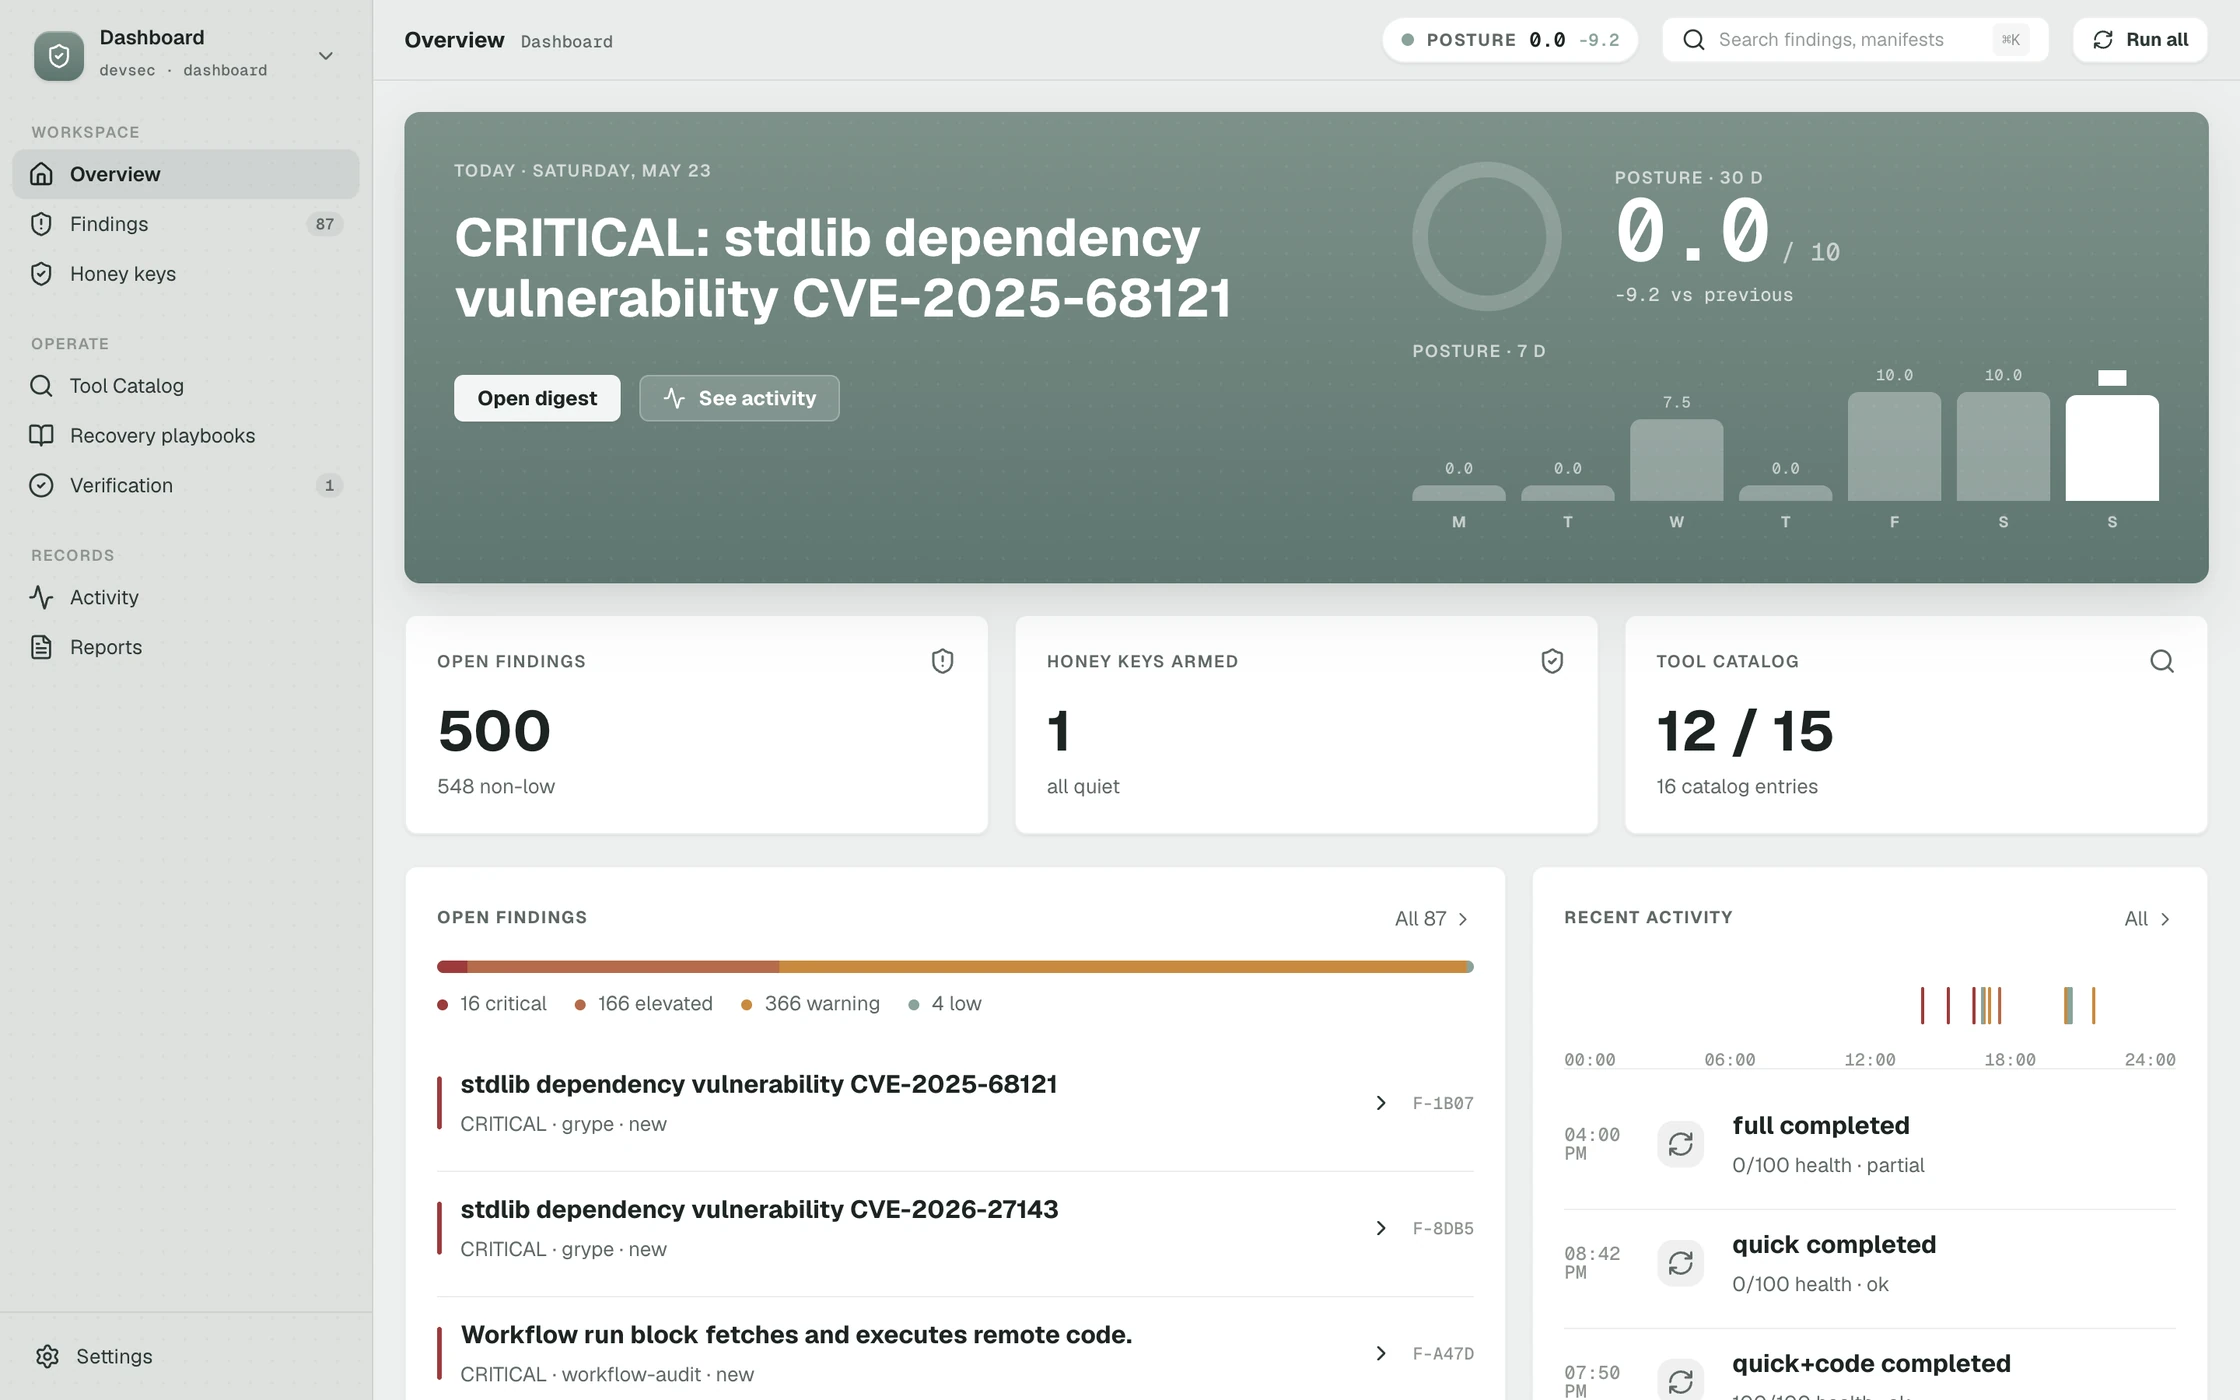
The DëvSec Overview: a sage band reading CRITICAL: stdlib dependency vulnerability CVE-2025-68121, a posture ring at 0.0 of 10 with minus 9.2 against the previous scan, seven daily bars, and cards for 500 open findings, 1 honey key armed and 12 of 15 tools in the catalog. Below, the open findings list with a severity bar of 16 critical, 166 elevated, 366 warning and 4 low, and a recent activity timeline.

Overview · dev-security · 23 May 2026

Posture · 30 d

0.0/ 10-9.2 vs previous

Posture · 7 d

0.0M0.0T7.5W0.0T10.0F10.0S10.0S

Open findings

  • 16 critical
  • 166 elevated
  • 366 warning
  • 4 low

Activity · 24 h

00:0006:0012:0018:0024:00

A calmer way to see what your repo needs.

Scans stay local

Run established open-source scanners against repos on your machine. Source and reports stay under your control.

Plain next actions

Scanner output is grouped into cases with severity, evidence, suggested fixes, and agent-ready handoff prompts.

Honest coverage

Missing tools, partial scans, and evidence gaps are shown directly instead of being hidden behind a misleading score.

02 · 32 seconds

Watch one scan, start to finish.

The trailer, without sound. Nothing in it is mocked.

03 · Cases

From 500 findings to one next action.

11

Scanners

run on the machine

500

Raw findings

deduplicated by fingerprint

87

Cases

risk, evidence, fix

3

Playbooks

steps and a time estimate

1

Next action

CRITICAL: stdlib CVE-2025-68121
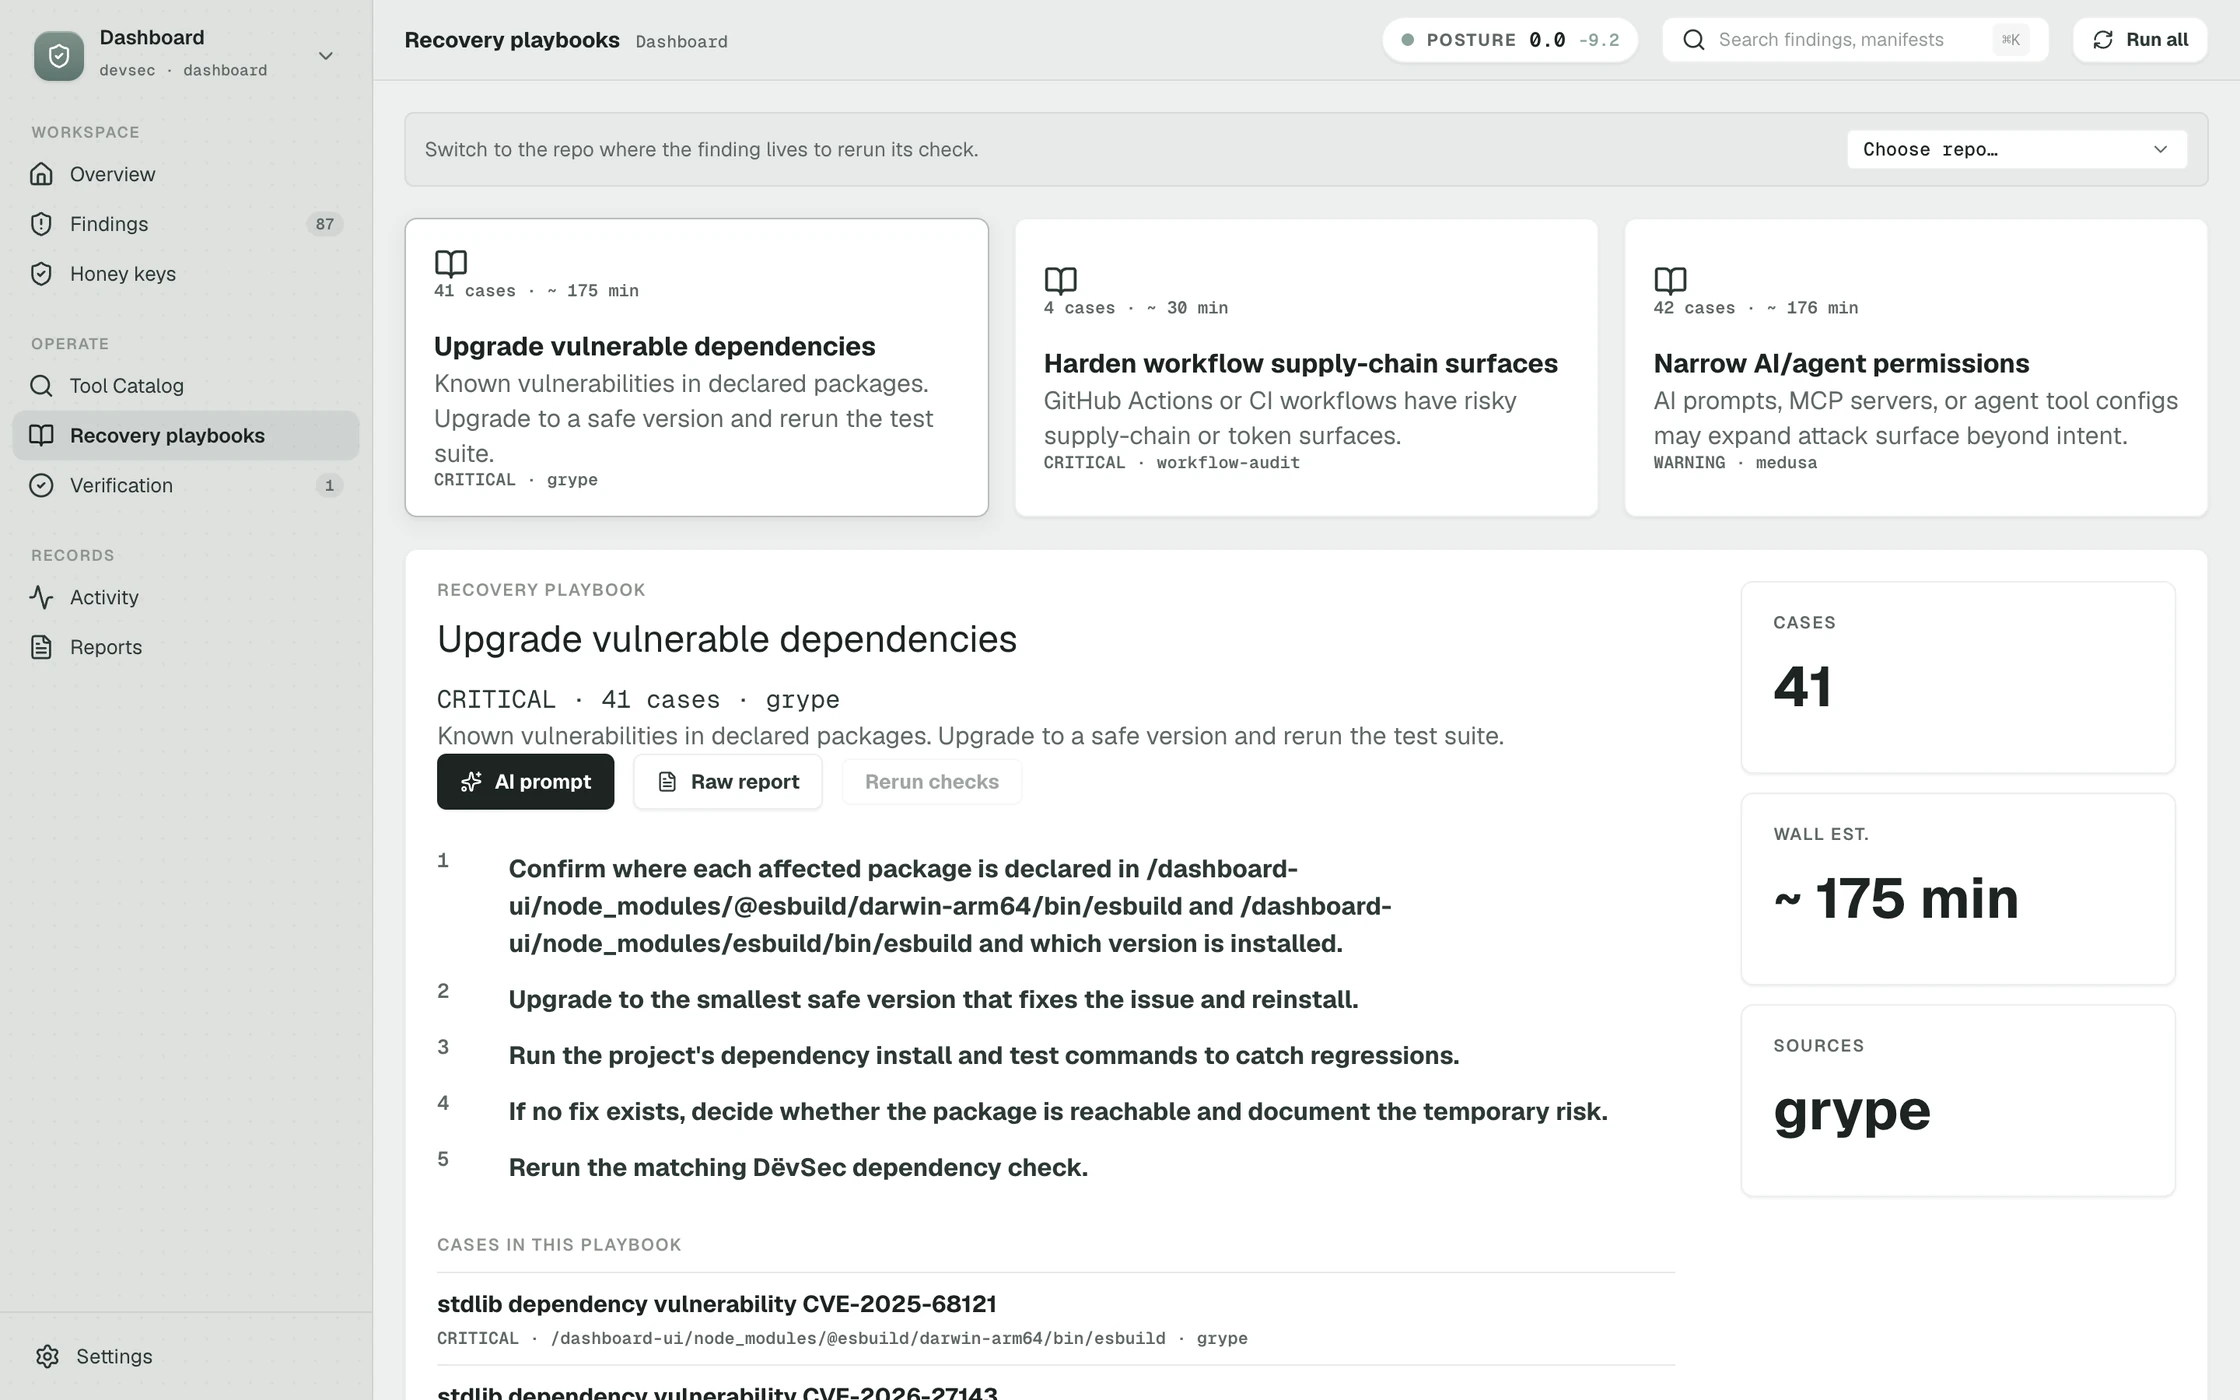
Recovery playbooks: three playbook cards, Upgrade vulnerable dependencies with 41 cases and about 175 minutes, Harden workflow supply-chain surfaces with 4 cases, Narrow AI/agent permissions with 42 cases. The first is open, showing five numbered steps, an AI prompt button and side cards for 41 cases, about 175 minutes, and the source scanner grype.

41 findings become one playbook.

One job of about 175 minutes, with numbered steps. Not forty-one tickets.

The handoff.

A prompt for the agent you already trust, written on the machine. Verify first, then fix.

AI prompt · ready to copy

F-1B07

stdlib dependency vulnerability CVE-2025-68121

Case: stdlib dependency vulnerability CVE-2025-68121
Risk: A resumed TLS handshake can succeed where it should
      have failed.
Evidence:
- grype: CVE-2025-68121 in the Go stdlib inside
  dashboard-ui/node_modules/@esbuild/darwin-arm64/bin/esbuild
- Go advisory GO-2026-4337: crypto/tls, fixed in go1.24.13,
  go1.25.7 and go1.26.0-rc.3
Verification steps:
- Confirm the scanner result against that binary.
- Decide whether this is exploitable here, not just theoretically.
Fix steps:
- Rebuild on a Go release the advisory lists as fixed.
- Re-run the matching DëvSec dependency check.

04 · Install

Start with a clone, not an account.

The shortest path is still the most honest one: install locally, scan a repo, then open the dashboard on 127.0.0.1.

Read the docs
DëvSec terminal

[01]$git clone https://github.com/Christian-Katzmann/dev-security.git

→ Repository cloned · workspace prepared

[02]$cd dev-security

→ Entered isolated audit directory

[03]$./install-security-observatory.sh

→ Scanner toolchain ready · dependency cache warmed

[04]$security-scan .

→ SBOM generated · secrets checked · CVEs resolved

[05]$security-scan dashboard

→ Dashboard on http://127.0.0.1:8765 · nothing left the machine

Eleven scanners, one contract.

Established open-source tools, each with a policy for network, credentials and file writes. A missing tool shows as missing.
Semgrepcode
Gitleakssecrets
TruffleHogsecrets
Trivydependencies · IaC
OSV-Scannerdependencies
Grypedependencies
SyftSBOM
Checkovinfrastructure as code
MedusaAI agents · MCP
ai-staticbuilt in
IOC-watchbuilt in
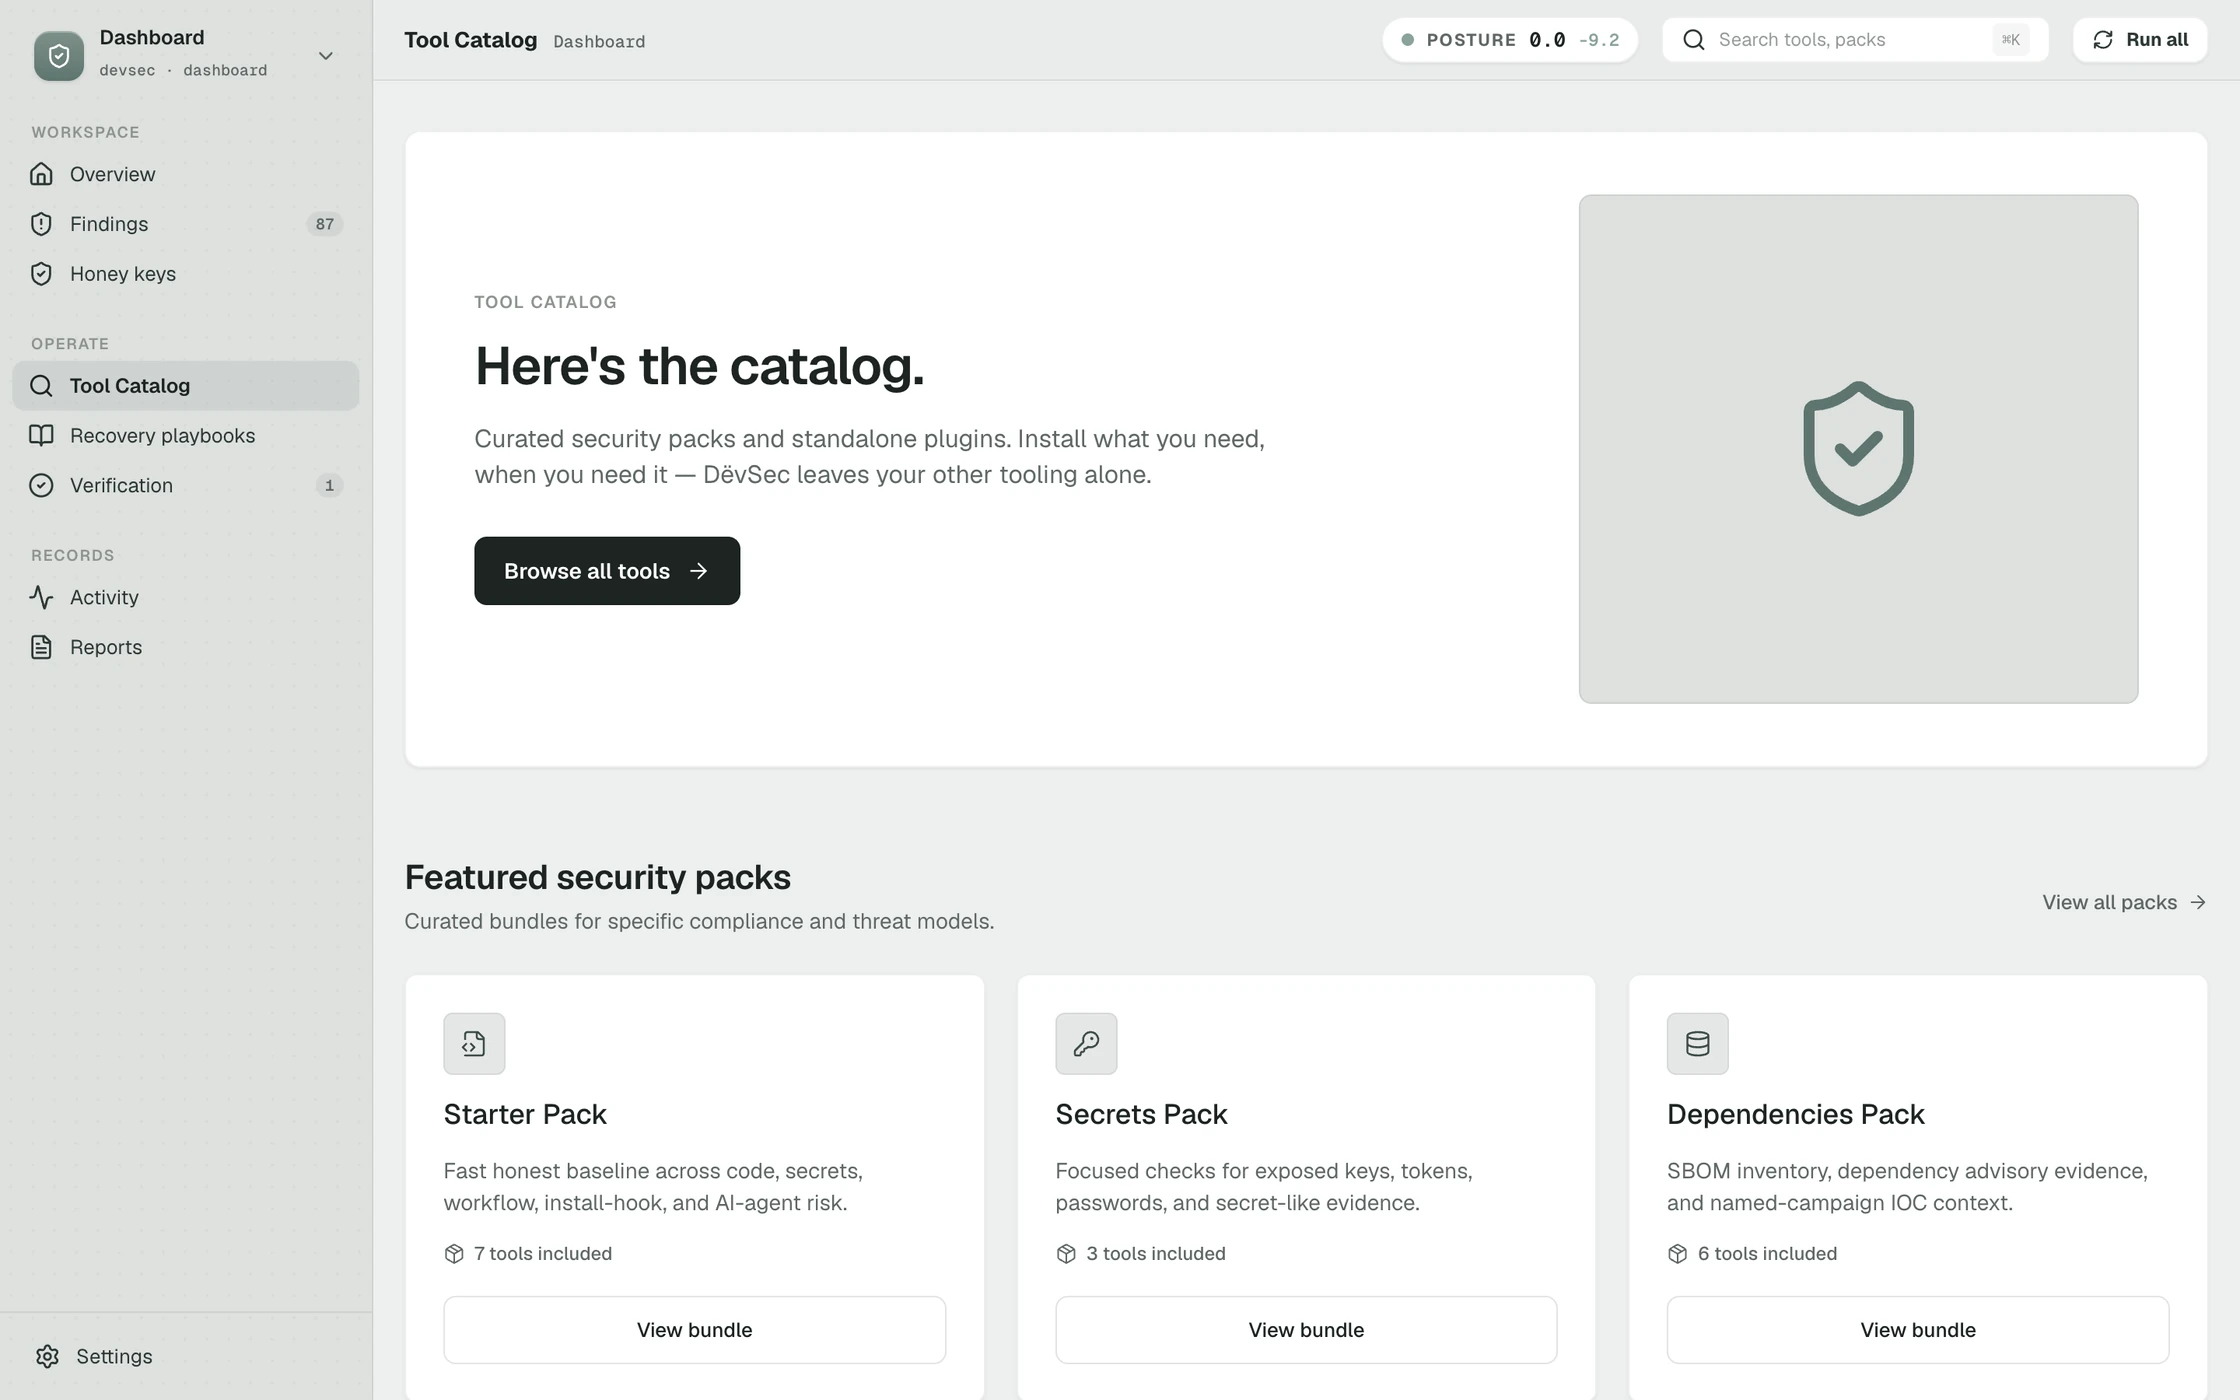
The Tool Catalog: a hero reading Here's the catalog, with curated security packs and standalone plugins, and three featured packs beneath it: Starter with 7 tools, Secrets with 3, Dependencies with 6.

Tool Catalog · 12 of 15 tools ready

05 · Honey keys

A secret that opens nothing, and says when it is touched.

A decoy key that authenticates to nothing. Use it, and the project turns critical.

Trace

  1. [00:01]decoy minted · reads as an internal API key
  2. [00:02]inserted · .devsec/honeykeys/legacy-prod-config.json
  3. [00:03]raw key discarded · hash kept
  4. [--:--]waiting
  5. [07:14]key used · source, path and user agent recorded
  6. [07:14]project → critical

What it refuses to do

Never commits the decoy
Refuses to overwrite an existing file
Refuses to write outside the selected repo
Stores only a hash of the raw key
A trip at 127.0.0.1 is never called a remote attacker

06 · Trust boundary

Where does the code go? Nowhere.

Scanners, history and dashboard stay on the machine. Four network paths exist, all off by default.

Your machine

  1. 01
    Local repothe clone you already have
  2. 02
    security-scan CLIPython, one command
  3. 03
    Local scannersSemgrep, Gitleaks, TruffleHog, Trivy, OSV-Scanner, Grype, Syft, Checkov, Medusa, built-in checks
  4. 04
    Normalizer and case builderone finding shape, then cases
  5. 05
    ~/.security-observatorySQLite: scan history, findings, cases
  6. 06
    127.0.0.1:8765the dashboard, bound to loopback
  7. 07
    You

No upload, no telemetry, no licence server, no cloud model.

Opt-ins · off by default

EPSS exploit probability
api.first.org
sends the CVE IDs found in your dependencies
OpenSSF Scorecard
api.scorecard.dev
sends the org/repo slugs of your dependencies
Platform posture
GitHub, with your token
sends the repo slug
Managed tool downloads
github.com releases
sends nothing about the repo

07 · Repository

Role
Product, design and engineering. Solo, directing AI agents.
Timeline
21 May to 24 July 2026. 230 commits.
Stack
Python CLI, SQLite, React and Vite dashboard, MCP server.
Tests
626, including one that proves no network call on the default path.
Licence
Apache 2.0
Status
0.2.0, open source.

Public repo

github.com

Christian-Katzmann

/dev-security

Local-first security observability for repositories that stay on your machine.

Remote

Christian-Katzmann/dev-security
Open repo
DëvSecSëcure By Design™